Hi everyone,
I would like to introduce my Update Monitor for ZimaOS.
The project started because I wanted a more detailed and reliable way to monitor updates for my Docker applications. Over time, it has grown into a much larger tool with update detection, automatic update policies, backups, encryption, restore functions and much more.
The application is still under development, but many important functions are already working.
Main Features
Docker Update Monitoring
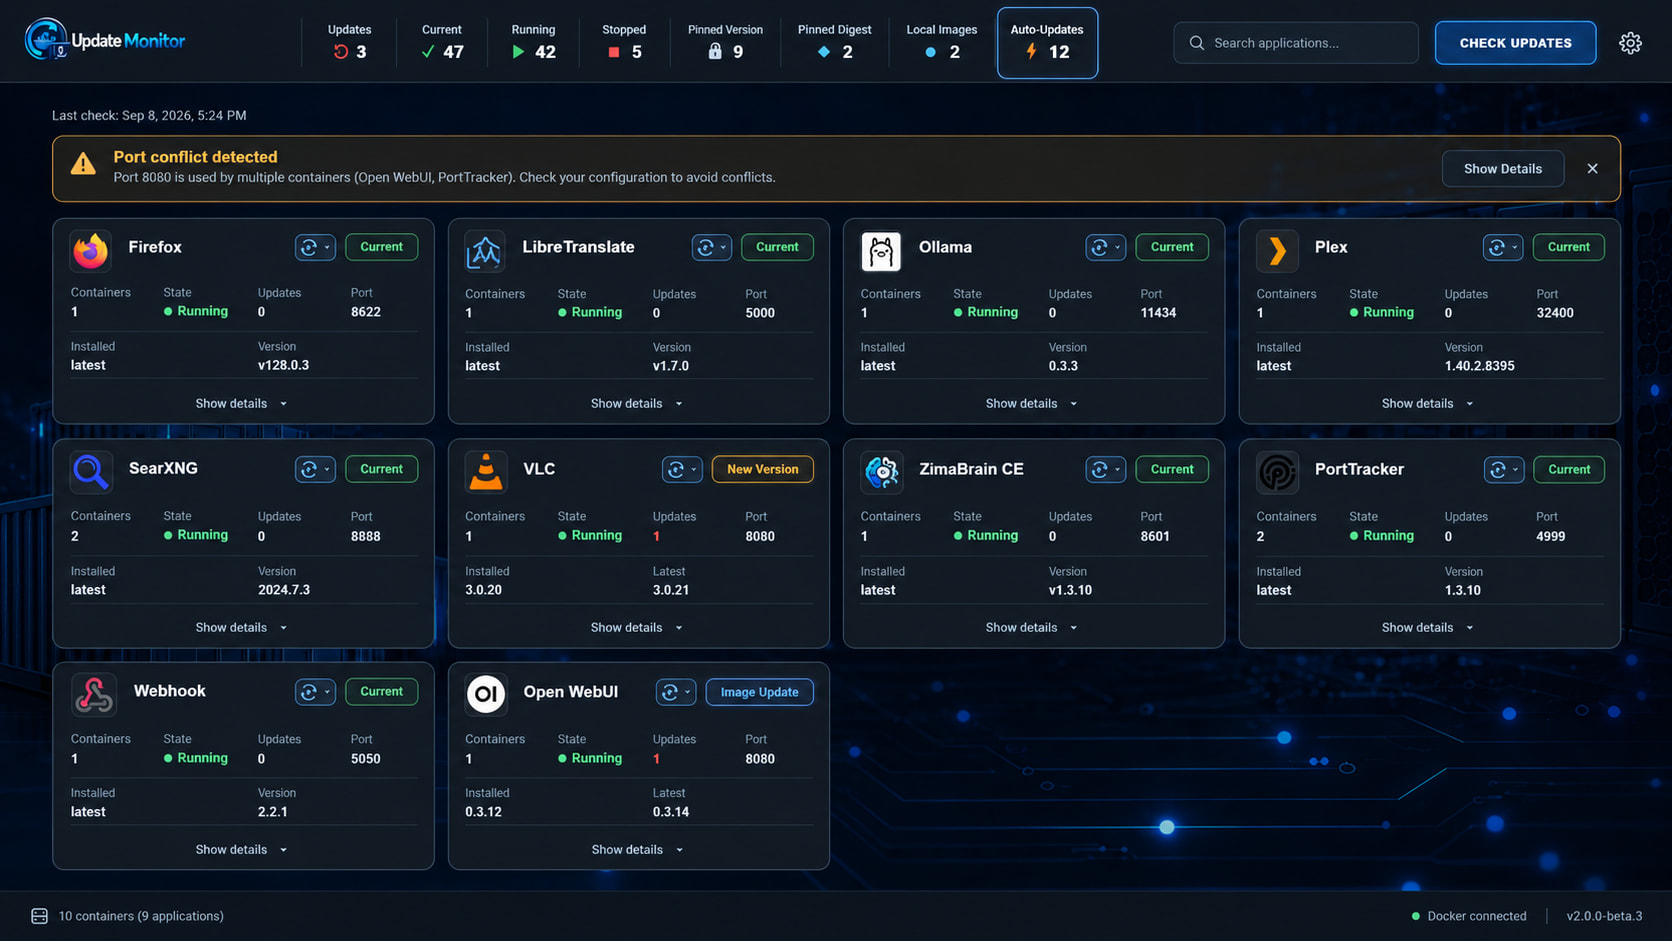
Update Monitor scans the installed Docker applications and displays their current update status.
It can show for example:
- Current
- New version available
- Docker image update available
- Pinned version / digest
- Local image
- Detection errors
The application also shows information such as:
- Installed version
- Available version
- Local image digest
- Remote digest
- Container
- Docker image
- Ports
- Current container state
- Project/source link
GitHub, Codeberg and other project sources can be detected where possible.
[Screenshot – Main Update Monitor overview]
Reliable Update Verification
After an update, Update Monitor does not simply assume that the installation was successful.
The update process is divided into separate phases:
Backup → Installation → Verification
After installing an update, only the affected application is checked again.
This means an automatic update cycle works approximately like this:
App 1 → Backup → Update → Verify App 1 → App 2 → Backup → Update → Verify App 2
It does not start a complete scan of every Docker application after each individual update.
Update Policies
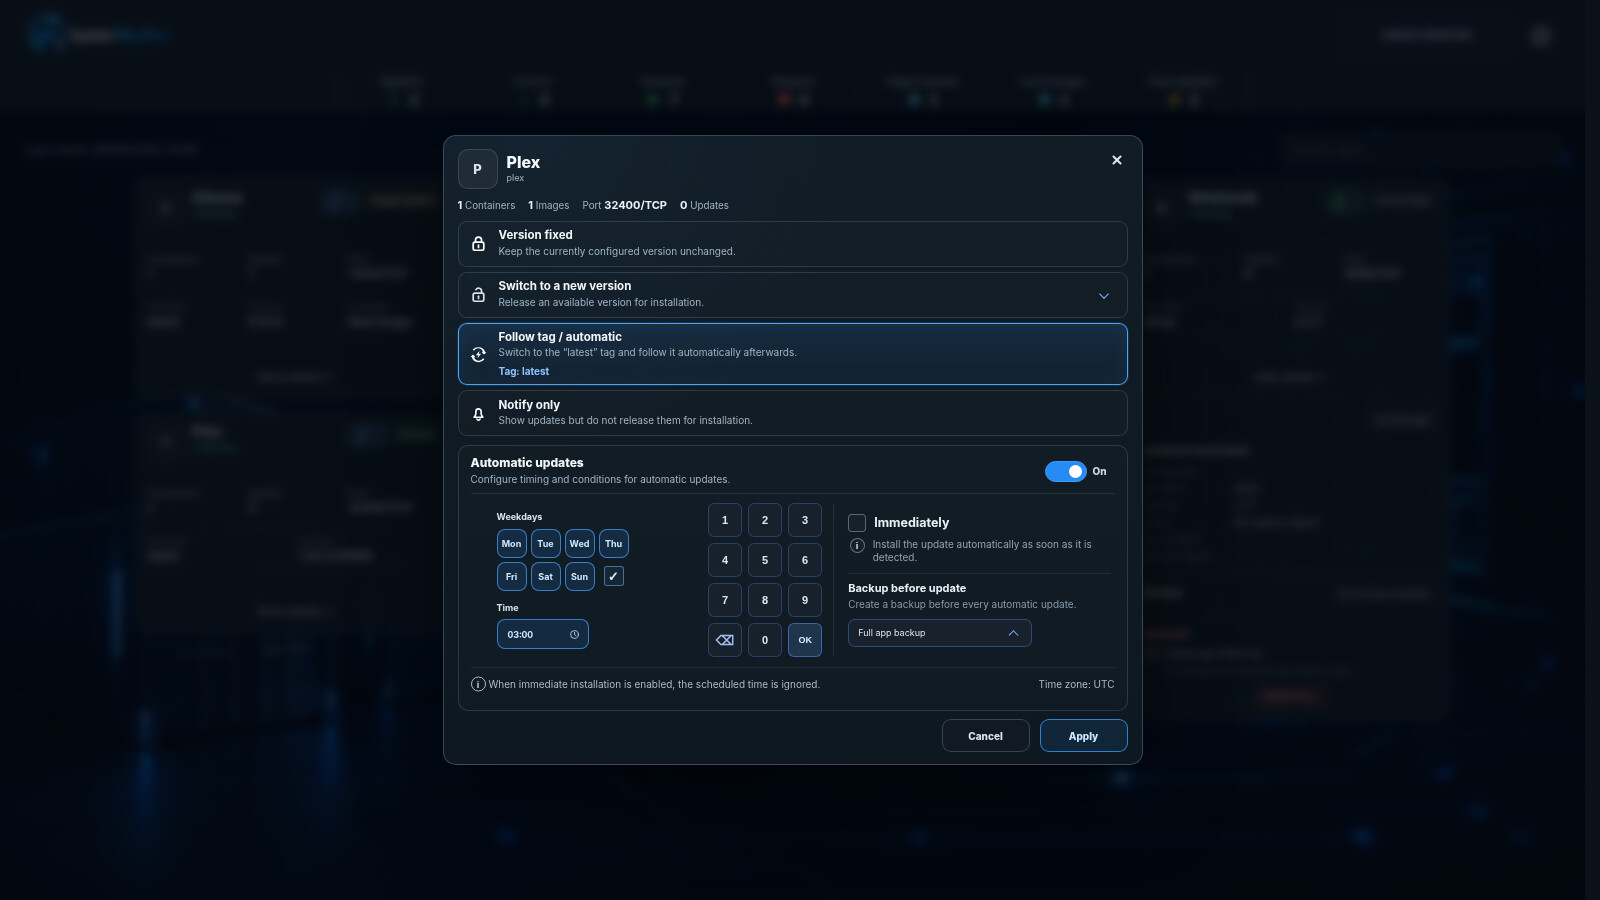
Each Docker application can have its own update policy.
Available options include:
- Fixed version
- Upgrade policy
- Follow updates
- Notification only
- Automatic updates
Automatic updates can also be scheduled individually by weekday and time.
There is also an immediate update option if the application should be updated as soon as an update is detected.
[Screenshot – Automatic Update settings]
Backup Before Updates
Before installing an update, Update Monitor can automatically create a backup.
Two backup types are available:
Quick Backup
Stores the information required to restore the previous Docker configuration/image state.
Full Backup
Additionally backs up the application data.
Backups are stored outside the Update Monitor AppData directory, for example:
/DATA/Backups/Update-Monitor/
Each application receives its own backup directory.
This is important because the backups remain available even if Update Monitor itself or another application is uninstalled.
Backups currently have a retention period of 5 days.
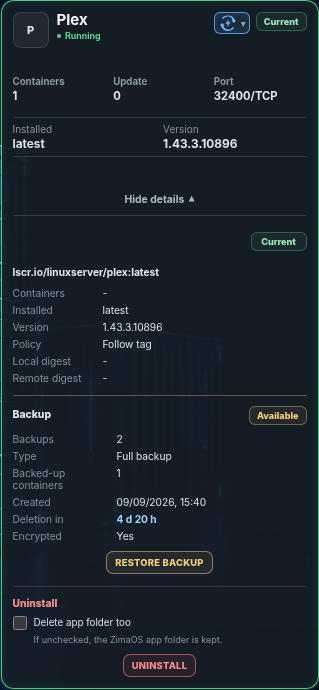
[Screenshot – Backup information inside application details]
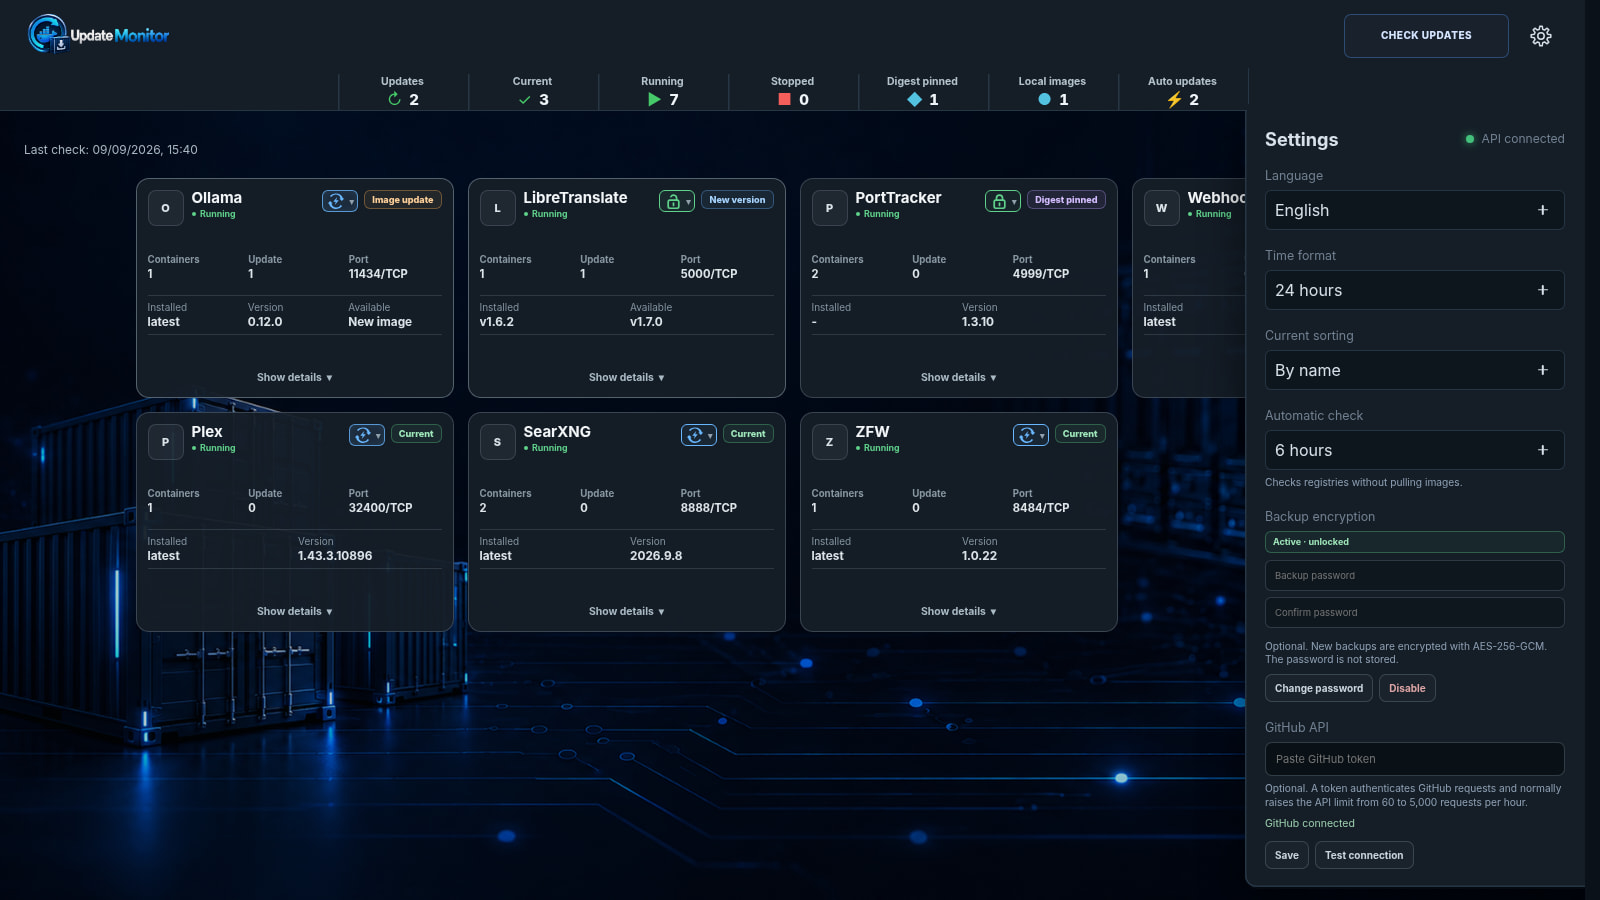
Backup Encryption
Backups can optionally be encrypted.
Encryption currently uses:
AES-256-GCM
The backup password itself is not stored.
When encryption is enabled, the Compose configuration and application data are packaged and encrypted into a file such as:
payload.umbackup.enc
Instead of leaving the application data directly readable inside the backup directory.
The interface shows whether backup encryption is:
- Disabled
- Active and unlocked
- Active and locked
The password can also be changed later.
[Screenshot – Backup Encryption settings]
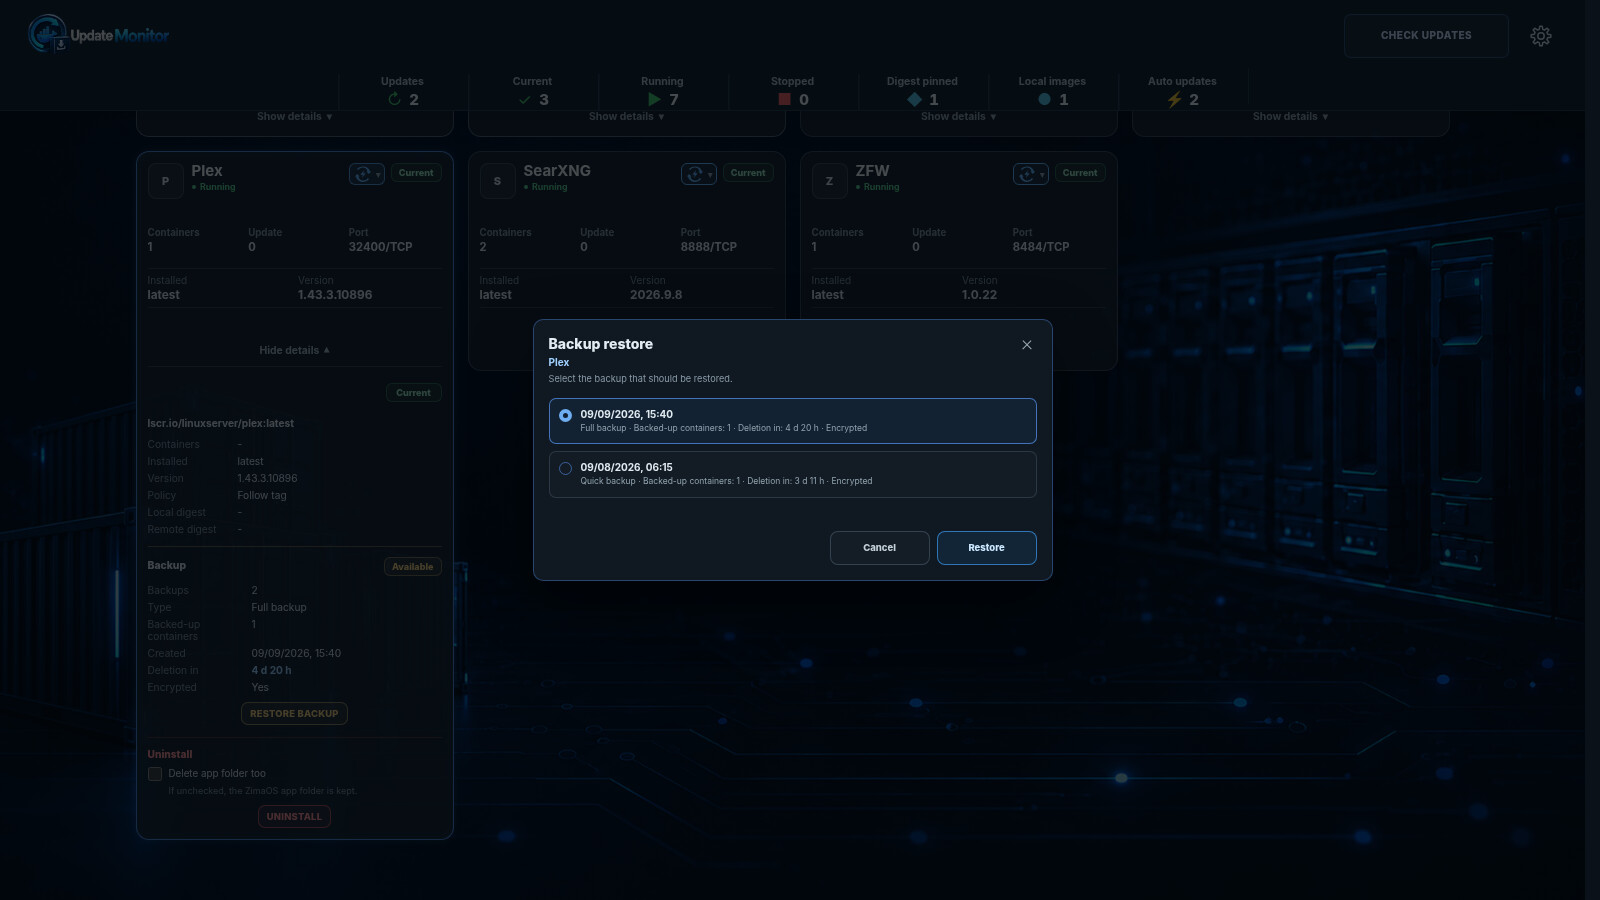
Backup Restore
Available backups can be displayed directly from the application details.
The restore dialog shows information including:
- Backup creation time
- Backup type
- Number of containers
- Encryption status
- Remaining retention time
A selected backup can then be restored directly through Update Monitor.
For a full backup, the application data is restored as well.
After the restore, Update Monitor performs another targeted verification of the affected Docker application.
[Screenshot – Restore Backup dialog]
Port Conflict Detection
Update Monitor can detect when different Docker applications use the same published port.
If a conflict is detected, a warning appears at the top of the interface.
Opening the warning shows:
- The affected port
- The applications using it
- The corresponding containers
This makes it easier to find Docker configuration conflicts.
Project Source Detection
Update Monitor tries to determine the original project/source behind a Docker image.
The long-term system is designed to use several sources instead of relying only on GitHub.
Detection can use Docker/OCI labels such as:
org.opencontainers.image.sourceorg.opencontainers.image.urlorg.opencontainers.image.documentationorg.label-schema.vcs-url
This allows the application to provide direct links to GitHub, Codeberg and other project pages when available.
GitHub API Support
A GitHub token can optionally be configured.
Without authentication, GitHub API requests are limited.
With a token, Update Monitor can use the higher authenticated API limit.
The interface displays:
- GitHub connection status
- API requests already used
- API request limit
The token can be tested and removed directly from the settings.
Responsive Interface
The interface is designed to adapt to different screen sizes rather than relying on fixed device lists.
I am testing it on:
- Desktop
- Tablet
- iPad
- Smartphone
- Portrait mode
- Landscape mode
The application details can be expanded directly inside each Docker card.
Status indicators use different colors so that the current state can be recognized quickly.
Current Status
The project is still actively being developed.
My main goal is to create a Docker update system for ZimaOS that is:
- Reliable
- Easy to understand
- Safe
- Transparent
- Suitable for both manual and automatic updates
The backup and restore system is especially important to me because an automatic update should not simply replace a working application without providing a way back.
There are still features and improvements planned for future versions.
Update Monitor is also intended to become part of a larger Monitor Suite, together with my existing Disk Monitor and potentially additional monitoring tools later.